
ASP.NET CORE MVC & jQuery: v13.3.0 .NET 8
Adding HTTP-Only to the XSRF-TOKEN cookie results in 400 (Bad Request) errors throughout the application. Followed "HTTP-Only Anti-Forgery Token in ASP.NET Zero" blog. https://aspnetzero.com/blog/http-only-anti-forgery-token-in-asp.net-zero..
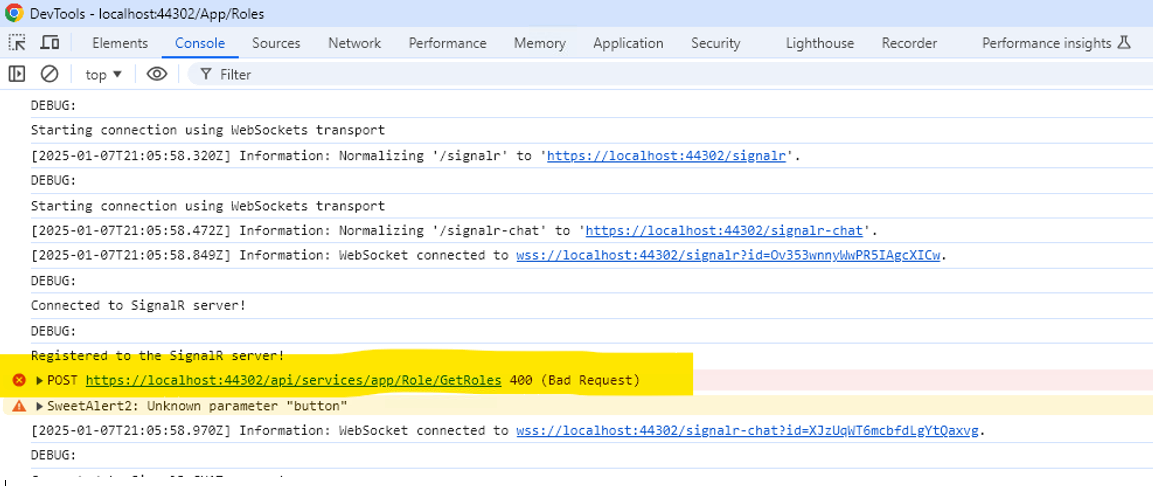
Attached is a screenshot from DevTools with a service call. All calls throughout the application result in a 400 (Bad Request) error.
18 Answer(s)
-
0
Hi @truist.software,
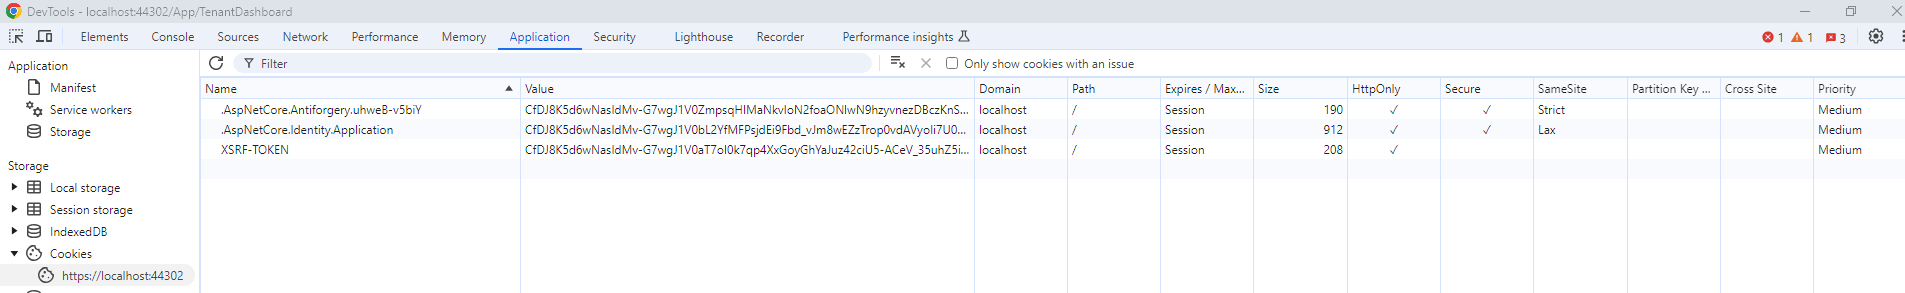
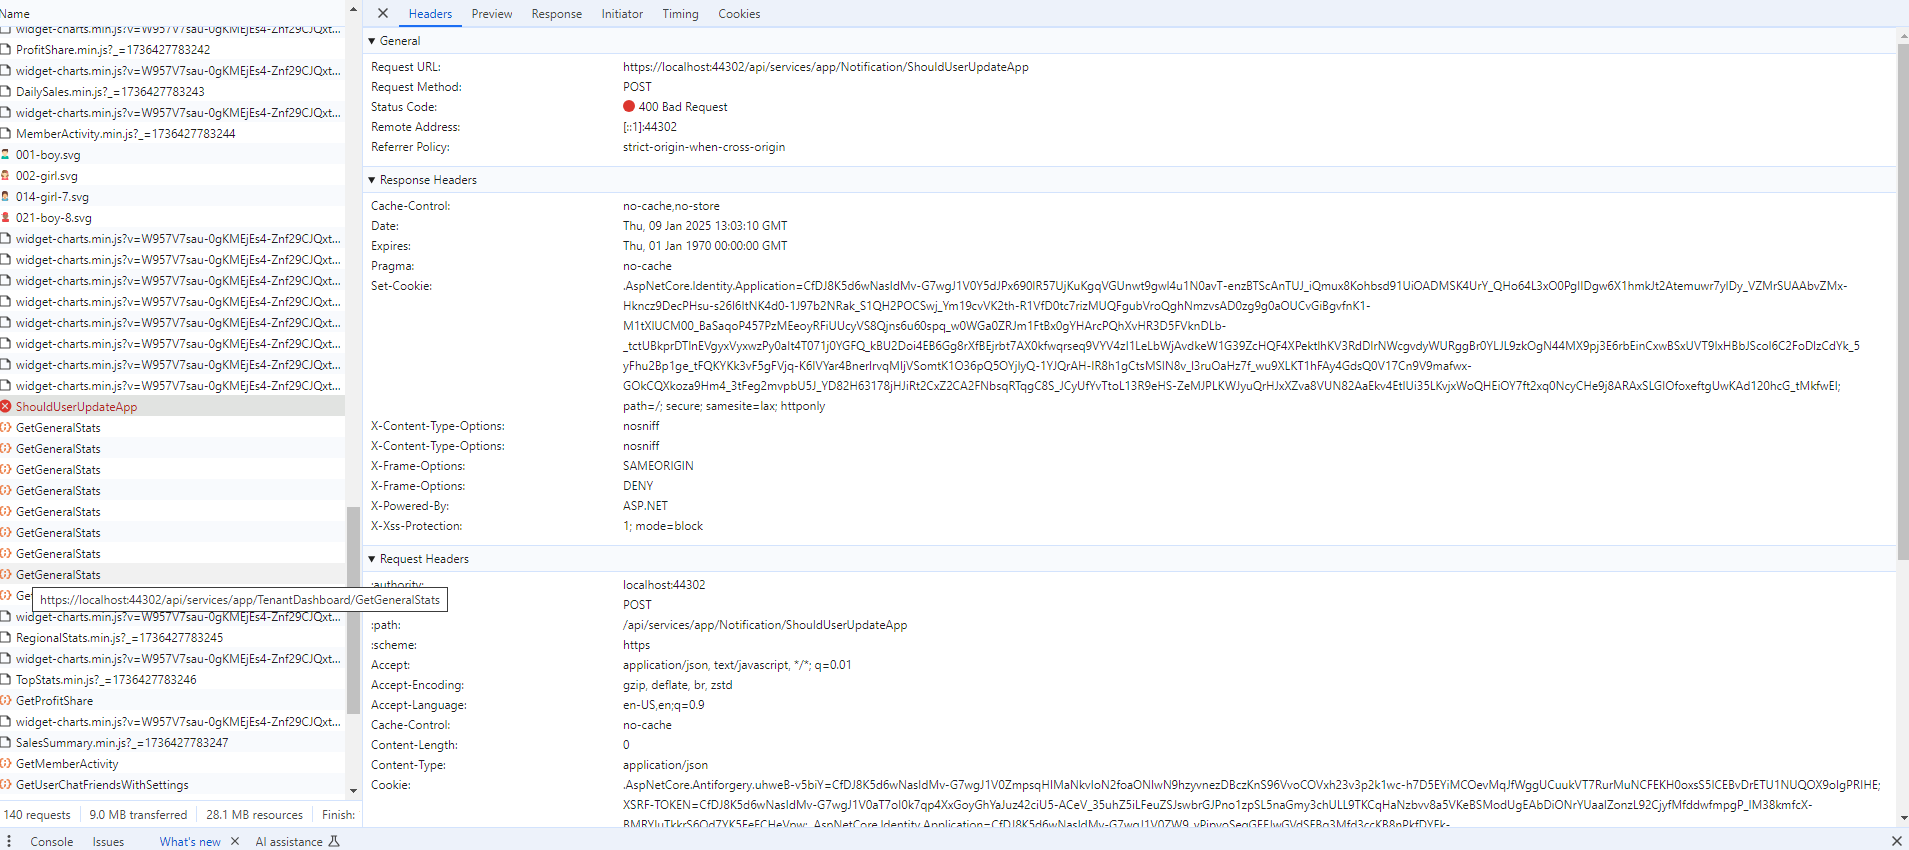
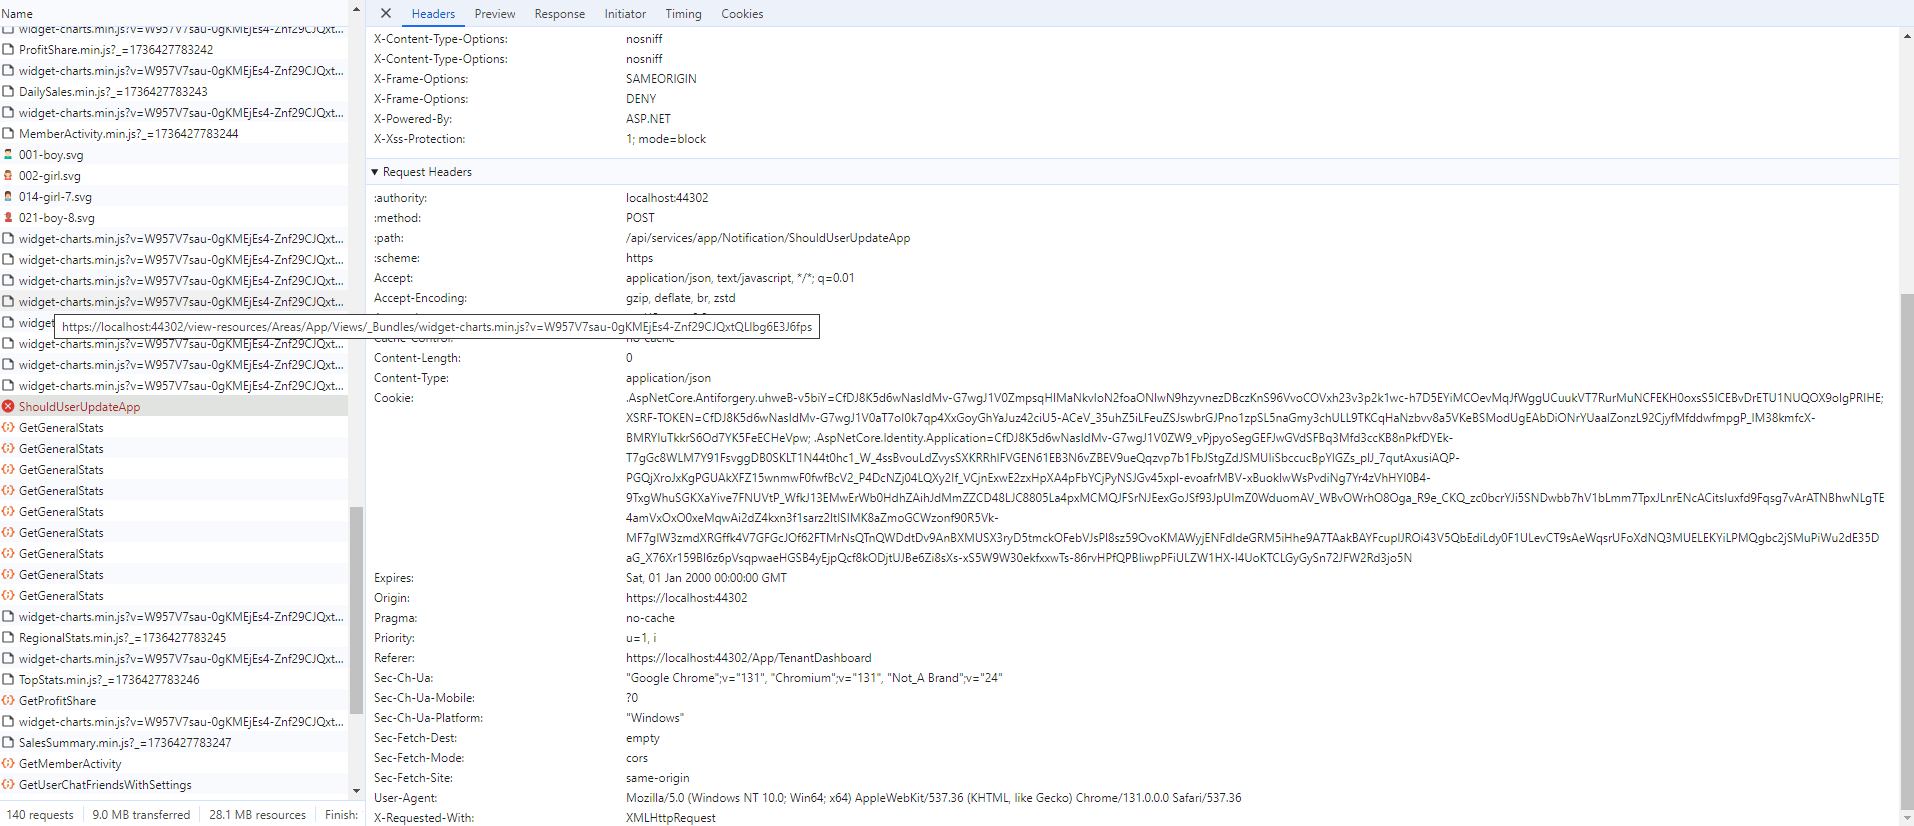
Can you share your request network and the cookies?
Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image) -
0
Updated with Cookies and Network information.
Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image) -
0
Hi @truist.software,
Do you have a cookie like this?

You may also have forgotten about using middleware.
 Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image)
-
0
As the screenshots show I do have the XSRF-TOKEN cookie and the HttpOnly attribute is set. As stated initially, I did follow the blog and have implemented the Middleware and configured it in Startup.cs which is why the cookie is set to HttpOnly. The issue is that setting this cookie to HttpOnly results in 400 Bad Requests errors when accessing the Application pages.
Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image) -
0
Hi @truist.software,
Could you share your project with [email protected] ?
Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image) -
0
I cannot share the project but I don't need to. If you just use: ASP.NET CORE MVC & jQuery: v13.3.0 .NET 8
straight from the download and you follow the blog https://aspnetzero.com/blog/http-only-anti-forgery-token-in-asp.net-zero you will see that the XSRF-TOKEN is set to HttpOnly per the blog but the application breaks with 400 Bad Request as you go through the different application features using the menu.
Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image) -
0
Hi @truist.software
Your problem of getting 400 error here has been solved in other versions. Here you can use the latest version 14.0.0 if you want. The problem you described does not occur in the latest version.
Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image) -
0
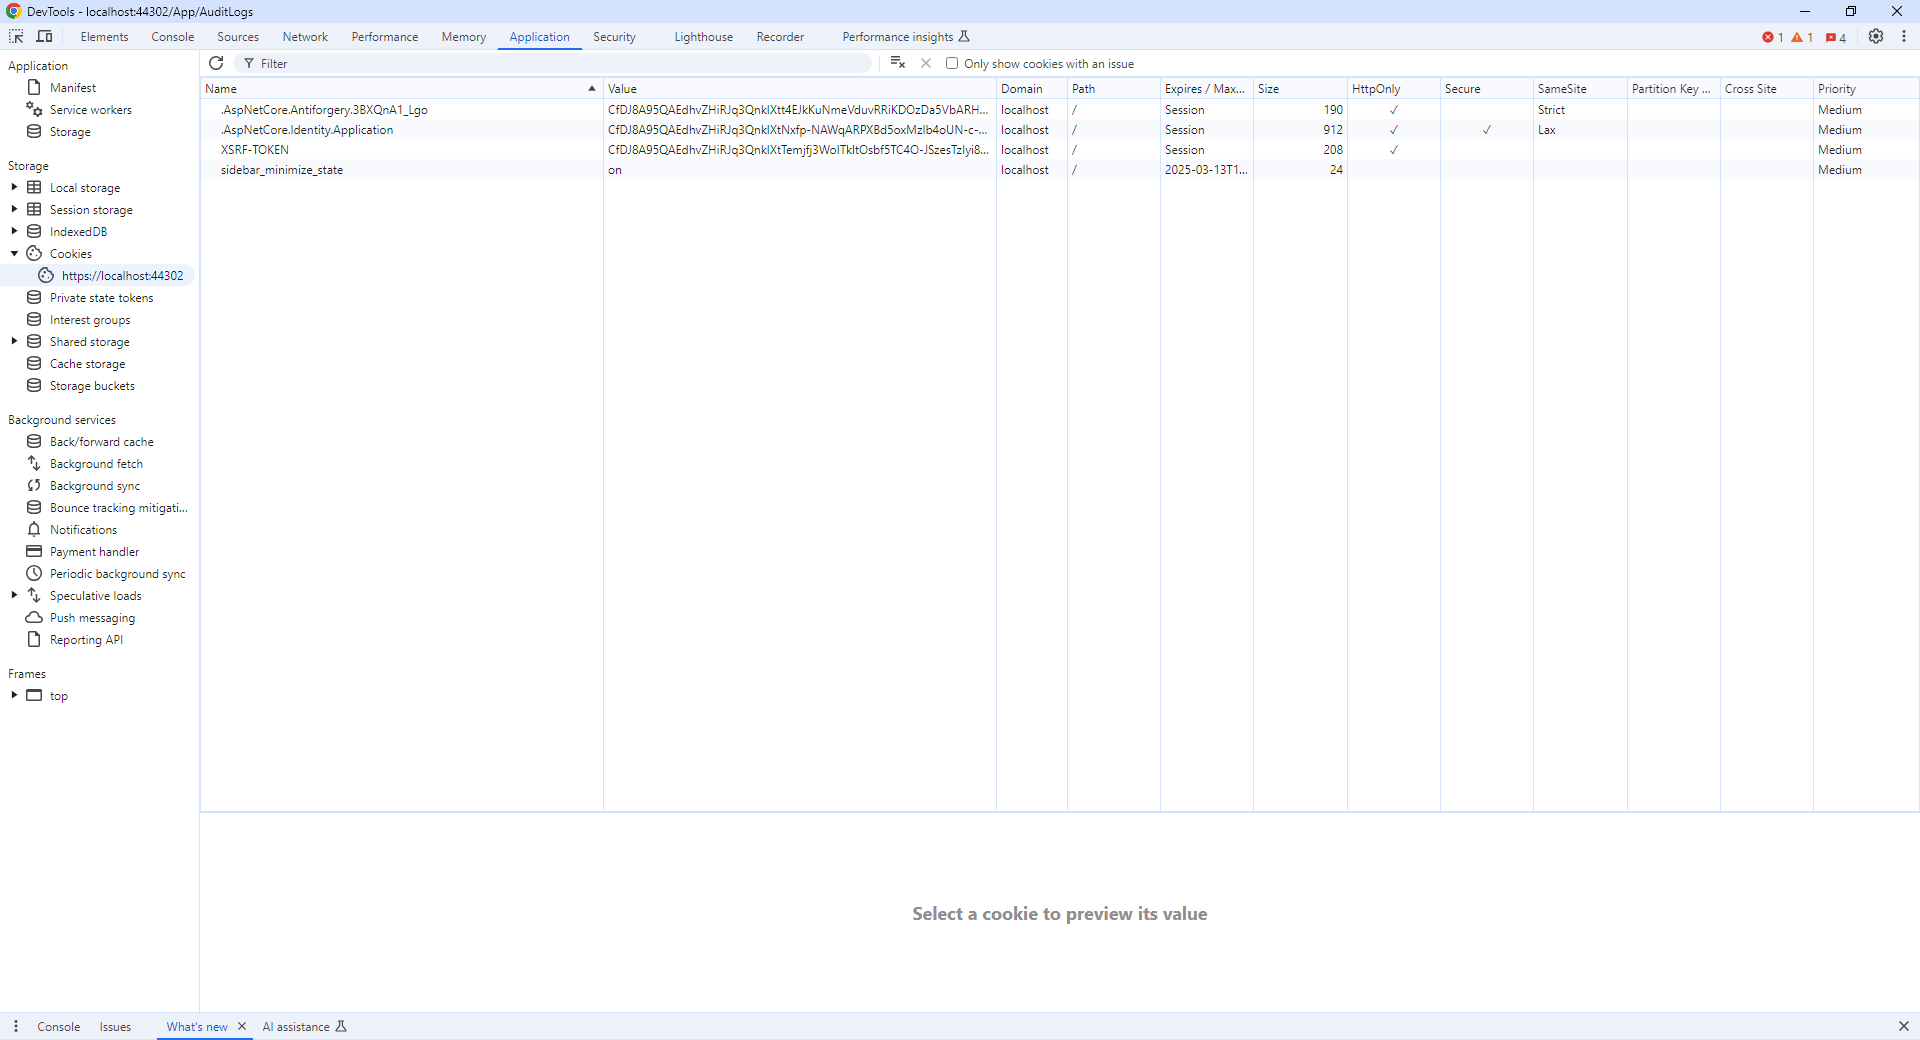
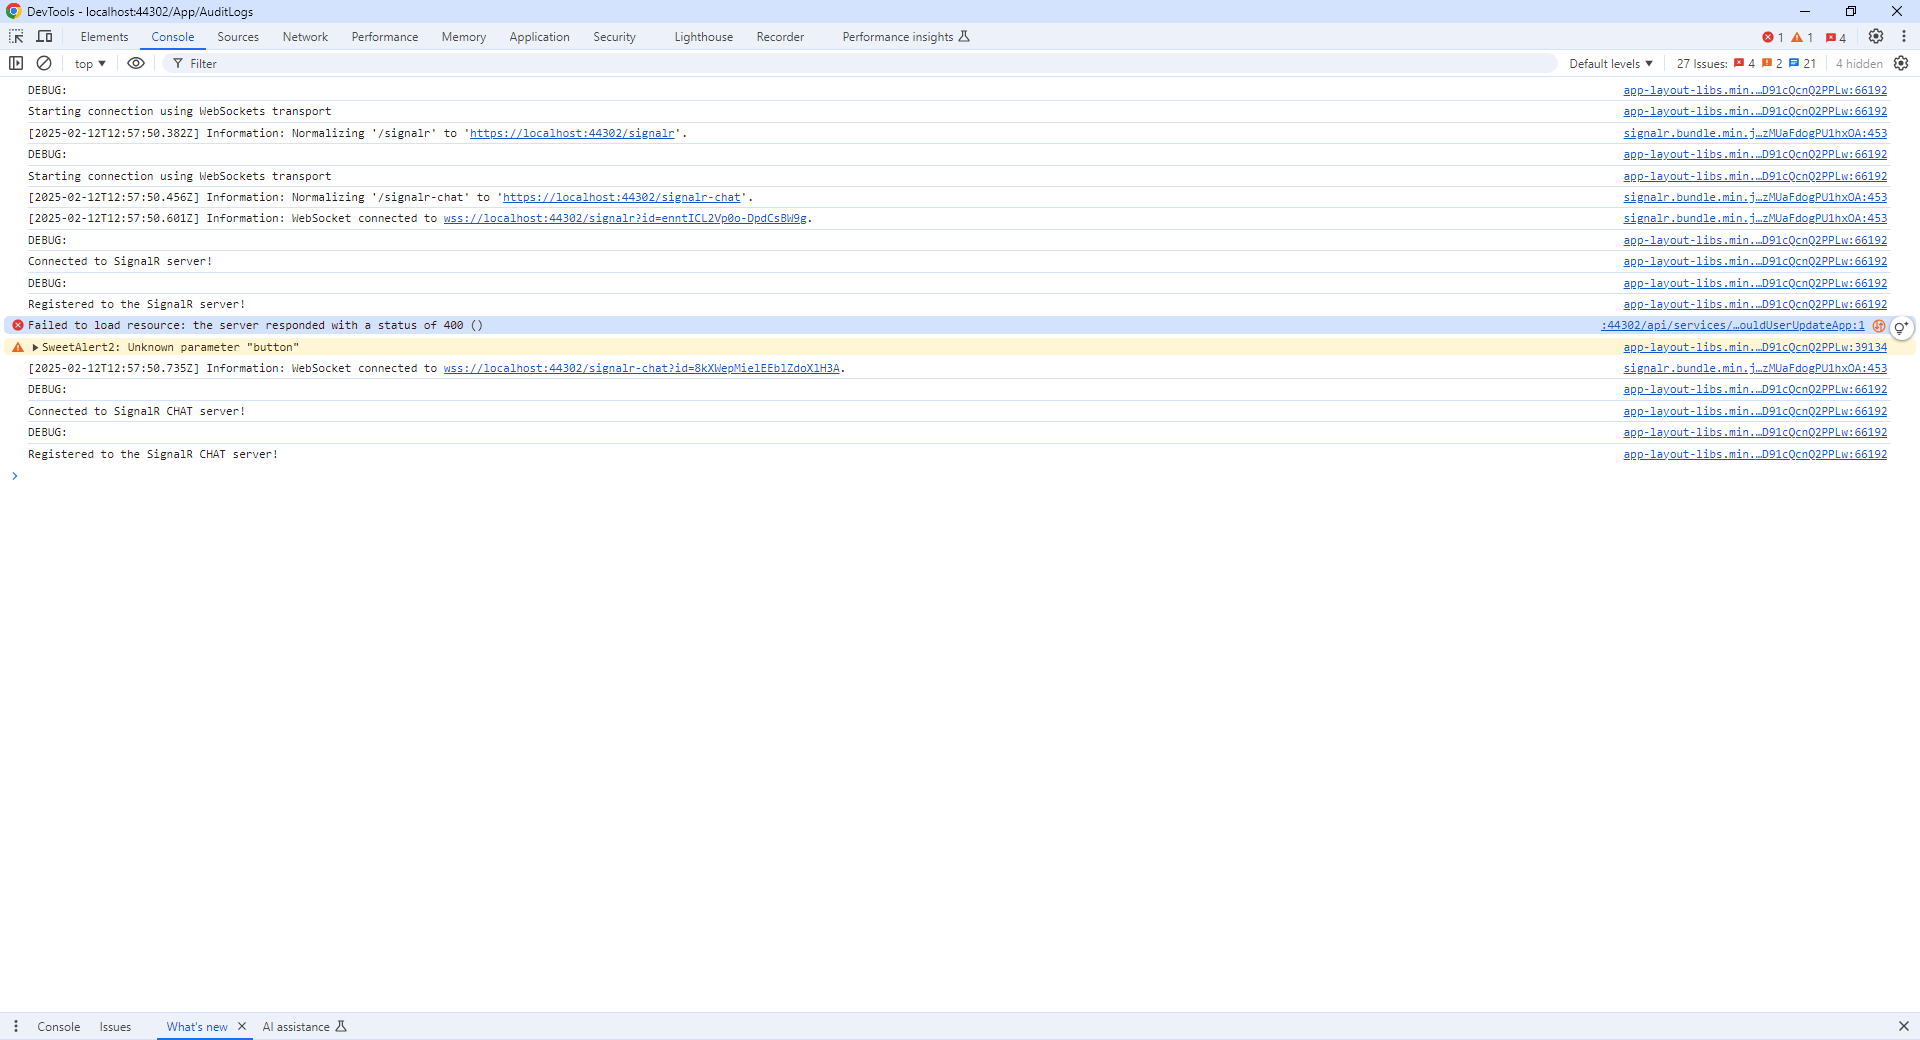
Using the latest version (see below) straight out of the box with no modifications other than implementing "HTTP-Only Anti-Forgery Token in ASP.NET Zero" exactly as presented in the blog. https://aspnetzero.com/blog/http-only-anti-forgery-token-in-asp.net-zero does not solve the issue as you stated above.
The XSRF-TOKEN is set with HttpOnly but the application throws 400 errors. Please advice.
ASP.NET CORE MVC & jQuery: v14.0.0 .NET 9
 Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image)
-
0
Hi @truist.software
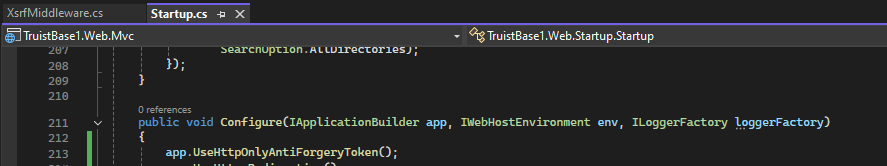
app.UseHttpOnlyAntiForgeryToken();After which ApplicationBuilder extension did you add the add operation? Make sure you add this at the top of theConfiguremethod inStartup.cs.public void Configure(IApplicationBuilder app, IWebHostEnvironment env, ILoggerFactory loggerFactory) { app.UseHttpOnlyAntiForgeryToken(); //Other }Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image) -
0
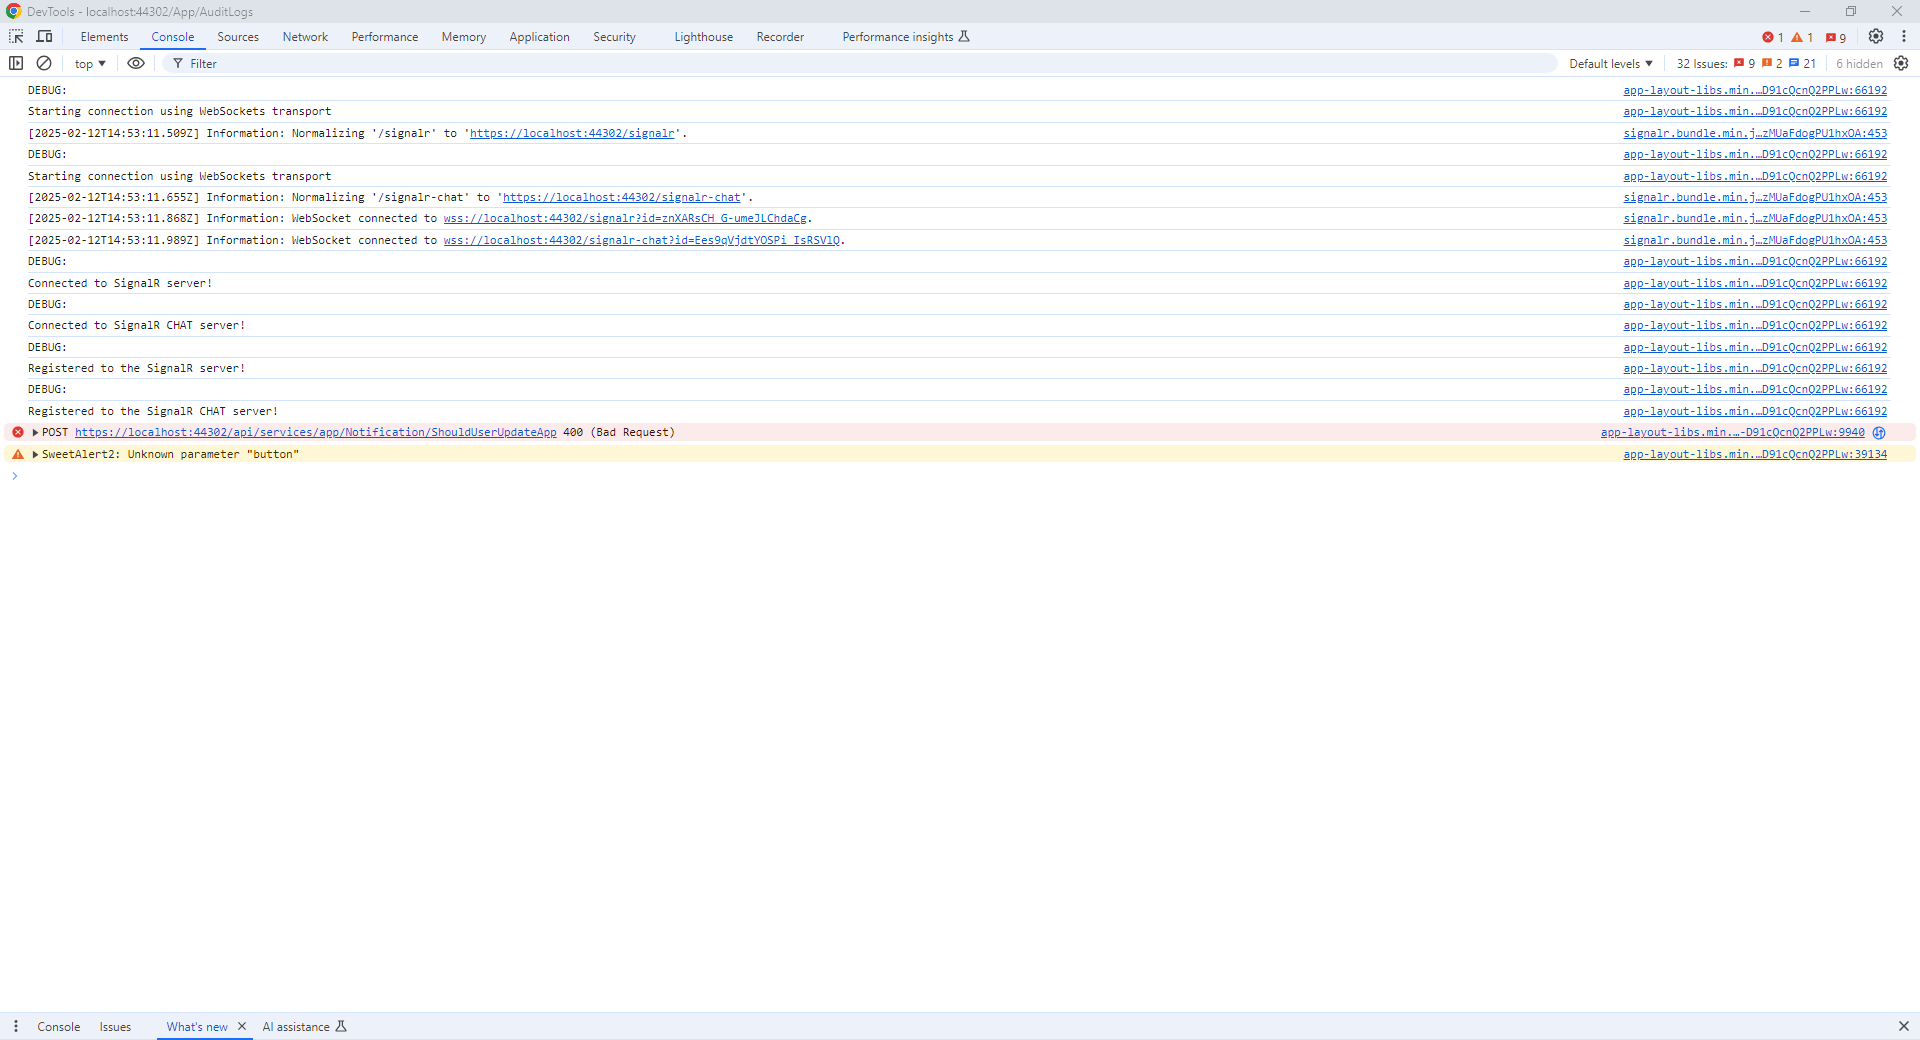
I have it at the top of the Configure method. It still errors out.
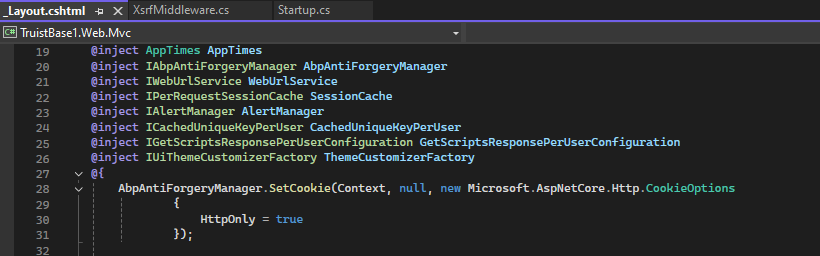 Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image)
-
0
Hi @truist.software
You need to apply this change in all
SetCookieusage in the project. Have you made this change for allSetCookieusage?Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image) -
0
Can you eloborate on "Have you made this change for all SetCookie usage?" I added the SetCookie logic in the _Layout.cshtml per the blog. Does it need to be added to other files/code? If so, where ?
Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image) -
0
Hi @truist.software
When you search for
"AbpAntiForgeryManager.SetCookie"in your project, you need to make the changes mentioned in the blog in 8 places. These files are as shown in the screenshot.Before
AbpAntiForgeryManager.SetCookie(Context);After
AbpAntiForgeryManager.SetCookie(Context, null, new CookieOptions
{
    HttpOnly = true
});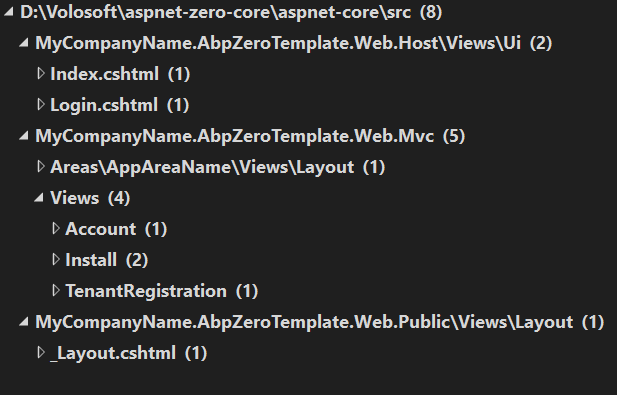
In the *.Web.Host project, you will only need to add the
"HttpOnly = true"setting to Index.cshtml under UI.Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image) -
0
The above suggestions continue to produce error. With your latest version implement the steps in https://aspnetzero.com/blog/http-only-anti-forgery-token-in-asp.net-zero and the suggested fixes above. I still get errors.

Log entry: INFO 2025-06-20 06:30:31,206 [26 ] c.Infrastructure.ControllerActionInvoker - Route matched with {area = "app", action = "GetUserChatFriendsWithSettings", controller = "Chat"}. Executing controller action with signature System.Threading.Tasks.Task`1[TruistBase1.Chat.Dto.GetUserChatFriendsWithSettingsOutput] GetUserChatFriendsWithSettings() on controller TruistBase1.Chat.ChatAppService (TruistBase1.Application). INFO 2025-06-20 06:30:31,206 [26 ] idateAntiforgeryTokenAuthorizationFilter - Skipping the execution of current filter as its not the most effective filter implementing the policy Microsoft.AspNetCore.Mvc.ViewFeatures.IAntiforgeryPolicy INFO 2025-06-20 06:30:31,207 [26 ] idateAntiforgeryTokenAuthorizationFilter - Antiforgery token validation failed. The required antiforgery header value "X-XSRF-TOKEN" is not present. | at Microsoft.AspNetCore.Antiforgery.DefaultAntiforgery.ValidateRequestAsync(HttpContext httpContext) at Microsoft.AspNetCore.Mvc.ViewFeatures.Filters.ValidateAntiforgeryTokenAuthorizationFilter.OnAuthorizationAsync(AuthorizationFilterContext context) Microsoft.AspNetCore.Antiforgery.AntiforgeryValidationException: The required antiforgery header value "X-XSRF-TOKEN" is not present. at Microsoft.AspNetCore.Antiforgery.DefaultAntiforgery.ValidateRequestAsync(HttpContext httpContext) at Microsoft.AspNetCore.Mvc.ViewFeatures.Filters.ValidateAntiforgeryTokenAuthorizationFilter.OnAuthorizationAsync(AuthorizationFilterContext context) INFO 2025-06-20 06:30:31,208 [26 ] c.Infrastructure.ControllerActionInvoker - Authorization failed for the request at filter 'Microsoft.AspNetCore.Mvc.ViewFeatures.Filters.ValidateAntiforgeryTokenAuthorizationFilter'. INFO 2025-06-20 06:30:31,208 [26 ] icrosoft.AspNetCore.Mvc.StatusCodeResult - Executing StatusCodeResult, setting HTTP status code 400 INFO 2025-06-20 06:30:31,208 [26 ] c.Infrastructure.ControllerActionInvoker - Executed action TruistBase1.Chat.ChatAppService.GetUserChatFriendsWithSettings (TruistBase1.Application) in 1.8984ms INFO 2025-06-20 06:30:31,208 [26 ] ft.AspNetCore.Routing.EndpointMiddleware - Executed endpoint 'TruistBase1.Chat.ChatAppService.GetUserChatFriendsWithSettings (TruistBase1.Application)'
Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image) -
0
Hi @truist.software
Thank you for your feedback. I will try to reproduce the issue, or look into how your issue can be resolved. I will get back to you as soon as possible if I encounter any problems.
Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image) -
0
Hi @truist.software
I checked the situation you mentioned in the latest version but did not encounter any errors. Here, you just need to ensure that you’ve added the
SetCookieconfiguration in the.cshtmlfiles and theUseHttpOnlyAntiForgeryTokenmiddleware. No service registration should be added for antiforgery. If you have addedAddAntiforgeryin theConfigureServicesmethod ofStartup.cs, you should remove it. If you haven't made such an addition and are still facing issues, please send your project to [email protected] so that we can provide a more specific solution. Thank you.Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image) -
0
I am still facing this issue. I am using .ASP.NET CORE MVC & jQuery: v14.1.0 .NET 9. I have done the following to a downloaded version of 14.1. There is no custom code only what is outlined in the blog post
- I have added SetCookie to all relevant files per (https://aspnetzero.com/blog/http-only-anti-forgery-token-in-asp.net-zero)
- I have added the XsrfMiddleware per (https://aspnetzero.com/blog/http-only-anti-forgery-token-in-asp.net-zero)
- I have set app.UseHttpOnlyAntiForgeryToken(); in the Configure method of the Startup.cs file.
This is the snippet from the Log file: INFO 2026-05-12 12:48:20,765 [54 ] ft.AspNetCore.Routing.EndpointMiddleware - Executing endpoint 'TruistBase1.Chat.ChatAppService.GetUserChatFriendsWithSettings (TruistBase1.Application)' INFO 2026-05-12 12:48:20,805 [54 ] c.Infrastructure.ControllerActionInvoker - Route matched with {area = "app", action = "GetUserChatFriendsWithSettings", controller = "Chat"}. Executing controller action with signature System.Threading.Tasks.Task`1[TruistBase1.Chat.Dto.GetUserChatFriendsWithSettingsOutput] GetUserChatFriendsWithSettings() on controller TruistBase1.Chat.ChatAppService (TruistBase1.Application). INFO 2026-05-12 12:48:20,805 [54 ] idateAntiforgeryTokenAuthorizationFilter - Skipping the execution of current filter as its not the most effective filter implementing the policy Microsoft.AspNetCore.Mvc.ViewFeatures.IAntiforgeryPolicy INFO 2026-05-12 12:48:21,101 [54 ] idateAntiforgeryTokenAuthorizationFilter - Antiforgery token validation failed. The required antiforgery header value "X-XSRF-TOKEN" is not present. | at Microsoft.AspNetCore.Antiforgery.DefaultAntiforgery.ValidateRequestAsync(HttpContext httpContext) at Microsoft.AspNetCore.Mvc.ViewFeatures.Filters.ValidateAntiforgeryTokenAuthorizationFilter.OnAuthorizationAsync(AuthorizationFilterContext context) Microsoft.AspNetCore.Antiforgery.AntiforgeryValidationException: The required antiforgery header value "X-XSRF-TOKEN" is not present. at Microsoft.AspNetCore.Antiforgery.DefaultAntiforgery.ValidateRequestAsync(HttpContext httpContext) at Microsoft.AspNetCore.Mvc.ViewFeatures.Filters.ValidateAntiforgeryTokenAuthorizationFilter.OnAuthorizationAsync(AuthorizationFilterContext context) INFO 2026-05-12 12:48:21,150 [54 ] c.Infrastructure.ControllerActionInvoker - Authorization failed for the request at filter 'Microsoft.AspNetCore.Mvc.ViewFeatures.Filters.ValidateAntiforgeryTokenAuthorizationFilter'. INFO 2026-05-12 12:48:21,160 [54 ] icrosoft.AspNetCore.Mvc.StatusCodeResult - Executing StatusCodeResult, setting HTTP status code 400 INFO 2026-05-12 12:48:21,160 [54 ] c.Infrastructure.ControllerActionInvoker - Executed action TruistBase1.Chat.ChatAppService.GetUserChatFriendsWithSettings (TruistBase1.Application) in 355.3928ms INFO 2026-05-12 12:48:21,160 [54 ] ft.AspNetCore.Routing.EndpointMiddleware - Executed endpoint 'TruistBase1.Chat.ChatAppService.GetUserChatFriendsWithSettings (TruistBase1.Application)' INFO 2026-05-12 12:48:21,162 [54 ] Microsoft.AspNetCore.Hosting.Diagnostics - Request finished HTTP/2 GET https://localhost:44302/api/services/app/Chat/GetUserChatFriendsWithSettings - 400 - - 895.9392ms
Cookies screenshot:
 Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image)
-
0
I am still facing this issue. I am using .ASP.NET CORE MVC & jQuery: v14.1.0 .NET 9. I have done the following to a downloaded version of 14.1. There is no custom code only what is outlined in the blog post
- I have added SetCookie to all relevant files per (https://aspnetzero.com/blog/http-only-anti-forgery-token-in-asp.net-zero)
- I have added the XsrfMiddleware per (https://aspnetzero.com/blog/http-only-anti-forgery-token-in-asp.net-zero)
- I have set app.UseHttpOnlyAntiForgeryToken(); in the Configure method of the Startup.cs file.
This is the snippet from the Log file: INFO 2026-05-12 12:48:20,765 [54 ] ft.AspNetCore.Routing.EndpointMiddleware - Executing endpoint 'TruistBase1.Chat.ChatAppService.GetUserChatFriendsWithSettings (TruistBase1.Application)' INFO 2026-05-12 12:48:20,805 [54 ] c.Infrastructure.ControllerActionInvoker - Route matched with {area = "app", action = "GetUserChatFriendsWithSettings", controller = "Chat"}. Executing controller action with signature System.Threading.Tasks.Task`1[TruistBase1.Chat.Dto.GetUserChatFriendsWithSettingsOutput] GetUserChatFriendsWithSettings() on controller TruistBase1.Chat.ChatAppService (TruistBase1.Application). INFO 2026-05-12 12:48:20,805 [54 ] idateAntiforgeryTokenAuthorizationFilter - Skipping the execution of current filter as its not the most effective filter implementing the policy Microsoft.AspNetCore.Mvc.ViewFeatures.IAntiforgeryPolicy INFO 2026-05-12 12:48:21,101 [54 ] idateAntiforgeryTokenAuthorizationFilter - Antiforgery token validation failed. The required antiforgery header value "X-XSRF-TOKEN" is not present. | at Microsoft.AspNetCore.Antiforgery.DefaultAntiforgery.ValidateRequestAsync(HttpContext httpContext) at Microsoft.AspNetCore.Mvc.ViewFeatures.Filters.ValidateAntiforgeryTokenAuthorizationFilter.OnAuthorizationAsync(AuthorizationFilterContext context) Microsoft.AspNetCore.Antiforgery.AntiforgeryValidationException: The required antiforgery header value "X-XSRF-TOKEN" is not present. at Microsoft.AspNetCore.Antiforgery.DefaultAntiforgery.ValidateRequestAsync(HttpContext httpContext) at Microsoft.AspNetCore.Mvc.ViewFeatures.Filters.ValidateAntiforgeryTokenAuthorizationFilter.OnAuthorizationAsync(AuthorizationFilterContext context) INFO 2026-05-12 12:48:21,150 [54 ] c.Infrastructure.ControllerActionInvoker - Authorization failed for the request at filter 'Microsoft.AspNetCore.Mvc.ViewFeatures.Filters.ValidateAntiforgeryTokenAuthorizationFilter'. INFO 2026-05-12 12:48:21,160 [54 ] icrosoft.AspNetCore.Mvc.StatusCodeResult - Executing StatusCodeResult, setting HTTP status code 400 INFO 2026-05-12 12:48:21,160 [54 ] c.Infrastructure.ControllerActionInvoker - Executed action TruistBase1.Chat.ChatAppService.GetUserChatFriendsWithSettings (TruistBase1.Application) in 355.3928ms INFO 2026-05-12 12:48:21,160 [54 ] ft.AspNetCore.Routing.EndpointMiddleware - Executed endpoint 'TruistBase1.Chat.ChatAppService.GetUserChatFriendsWithSettings (TruistBase1.Application)' INFO 2026-05-12 12:48:21,162 [54 ] Microsoft.AspNetCore.Hosting.Diagnostics - Request finished HTTP/2 GET https://localhost:44302/api/services/app/Chat/GetUserChatFriendsWithSettings - 400 - - 895.9392ms
Cookies screenshot:
Markdown is supportedCopy & paste or drag & drop images (max 30 MB per image)

